October 2026 | IT Support for Engineering Firms Salt Lake City | AI Threats | Halloween Cybersecurity
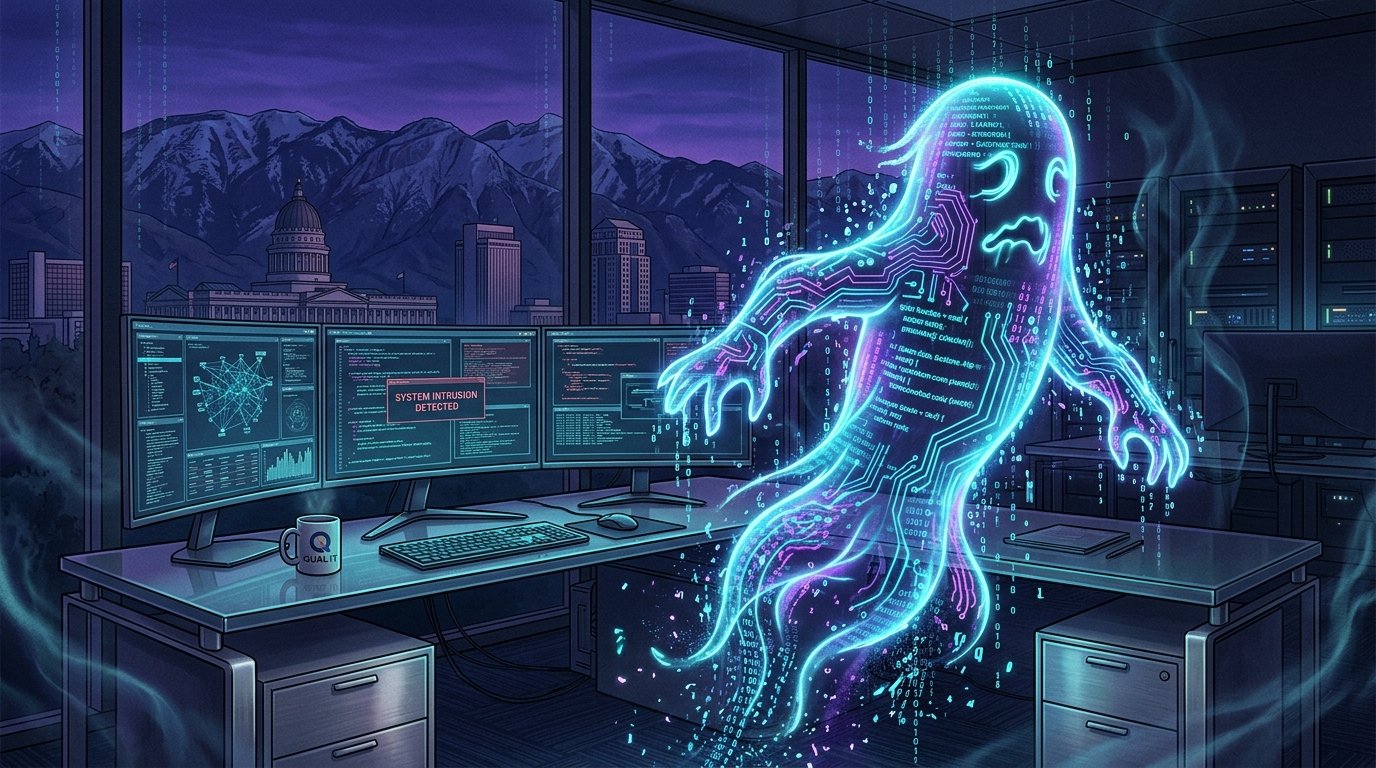
Look at any Salt Lake City neighborhood this Halloween and you'll see plenty of monsters roaming the streets — all costume, no threat. The threats facing your engineering firm work in reverse: no costume drama, all substance. They arrive dressed as routine project correspondence, familiar voices and helpful tools.
While firms like yours evaluate AI to speed up calculations, drafting and documentation, cybercriminals are using the same technology to give old scams new precision. The right IT support and a few documented procedures mean your engineering team doesn't have to be expert scam-spotters to stay safe. Garlic won't help you here — but a written verification procedure will. Let's run through the threat categories, Halloween taxonomy included.
AI Shapeshifters: Sounding Right Isn't Enough Anymore
Video and audio used to be a reliable way to distinguish a real person from an impersonator. Now, with AI, scammers can convincingly reproduce a voice from a few minutes of sample audio — and engineering firms publish plenty of it in webinars, project interviews and conference talks.
Picture the failure mode: a project manager gets a voicemail that sounds exactly like a principal, or like a contact at a client agency, authorizing a change to a subconsultant's payment details or requesting an urgent file transfer of design deliverables. Even if you can spot AI-generated audio today, those artifacts are being engineered out quickly. Many "AI tells" your team learned last year are already obsolete.
Instead of depending on individual detection — a control that degrades as the technology improves — rely on what can't be faked: documented verification procedures for any sensitive action, like payment changes, wire transfers or access grants. A shapeshifter can fool your ears, but it can't complete a call-back to a known number or satisfy multi-factor authentication.
AI Mummies: Old Scams Wrapped in New Cloth
In past years, phishing messages had spelling and grammatical mistakes that made them easy to spot. Typos, generic greetings and overused urgency became the red flags employees were trained to look for.
Those same scams have far better wrappings now. Perfect spelling, correct project terminology and plausible formatting give them an authority many readers won't question — a flawless notice that looks like DOT correspondence, a fabricated RFI response, or a counterfeit transmittal pointing to "revised drawings" behind a credential-harvesting login page.
Like a mummy in fresh linen, the underlying scam is as old as ever — only the disguise has improved. Train your engineering team to evaluate the request itself, not the polish of the message: Is this how this agency actually issues notices? Does this workflow normally arrive by email? Would this contact really send a new login link? Don't relax just because a message gets the project number right and reads cleanly.
AI Vampires: Never Invite Them In
In vampire lore, the creature cannot enter without an invitation. Unvetted AI tools operate on the same rule — and the invitation usually comes from your own staff, with good intentions.
When engineers use AI tools that haven't been approved by the firm — a phenomenon known as shadow IT — there are boundless opportunities to expose sensitive information. An unapproved AI tool can't open your project server on its own. But it won't stop a well-meaning engineer from pasting proprietary calculations, specification sections or details from a government project into a prompt field and asking for a summary or a check.
For an engineering firm, that's not just a privacy question — it can be a contract violation, and on defense-related work it can be a CMMC violation, the moment controlled information leaves your approved environment. If you can't answer where that information goes, where it's stored and what the tool's operator can do with it, it's not a tool that should be invited anywhere near your project files and engineering documents.
The Best Defense Against AI Monsters? Better Rules
Advancements in AI have made deception cheaper to produce, faster to deploy and more convincing — even to trained eyes. But detection is the wrong control to depend on when the failure rate rises every quarter. Documented procedures don't degrade. If your engineering team internalizes a few precise habits, even the most sophisticated disguises won't trip them up:
- Verify sensitive requests — payment changes, wire transfers, access grants — through a second, known channel. Always, no exceptions, no matter how senior the voice sounds.
- Judge messages by what they ask for, not how polished they look.
- Use only firm-approved AI tools, and never paste calculations, specs, client data or government project information into unapproved ones.
- Maintain a written approved-tool policy so "approved" is a documented list, not a judgment call.
- Make reporting suspicious activity fast, easy and blame-free.
Simple rules, consistently followed and written down, beat sophisticated detection skills every time. That's an argument any engineer will recognize: design the procedure so the system stays safe even when individual judgment fails.
Frequently Asked Questions
What are AI-powered cyber threats?
They're traditional attacks — phishing, impersonation, fraud — enhanced by AI: deepfake voice and video, flawlessly written scam emails dressed as agency correspondence or RFI responses and automated targeting. The underlying scams are old; the disguises are dramatically better.
How can engineering firms protect against deepfake and AI scams?
Build verification procedures that don't depend on recognizing fakes: documented call-back verification for payment and account changes, multi-factor authentication, a written approved-tool policy for AI use and training focused on request red flags rather than message quality. For firms with government contracts, align those procedures with CMMC requirements from the start.
Do you offer IT support for engineering firms and technical consultancies in Salt Lake City?
Yes. Qual IT provides IT support for engineering firms in Salt Lake City and along the Wasatch Front — managed IT services, cybersecurity, employee security awareness training, backup and disaster recovery for project archives, AI-use policy guidance and CMMC readiness support. We work with Salt Lake City engineering firms to protect project data and support technical workflows.
Know Where Your Gaps Are Before the Monsters Find Them
Need help protecting your firm against AI-enabled threats coming for your designs and project data? We'll discuss how your engineers are using AI, how sensitive requests are verified, how project files and engineering documents move between your firm and its subconsultants and what protections you already have in place. You'll leave with a clear, documented picture of where your biggest gaps are — no guesswork, and nothing left to superstition this Halloween season.
Schedule a free 10-minute discovery call with Qual IT. Book your discovery call here.