October 2026 | IT Support for Dental Offices Salt Lake City | Security Culture | Team Awareness
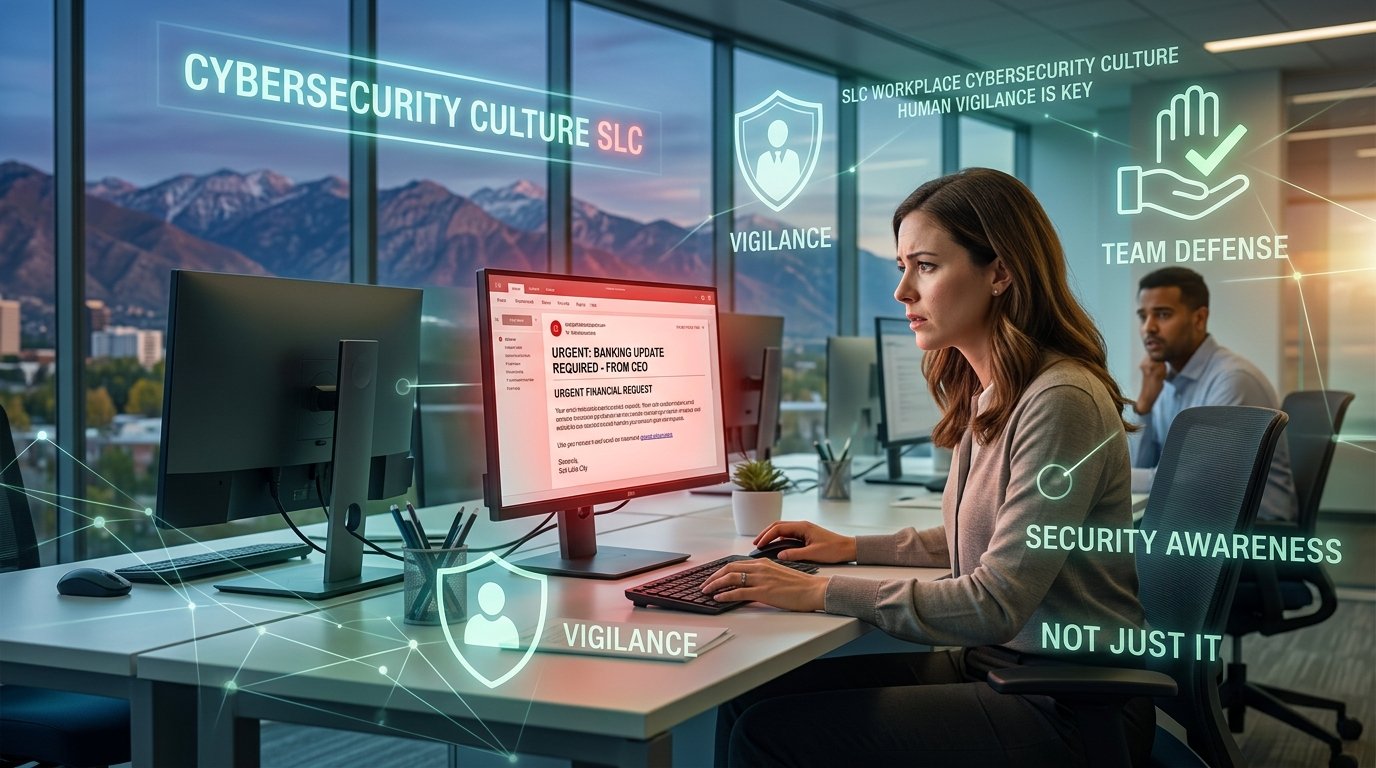
It's 4:17 on a Friday afternoon at a Salt Lake City dental practice.
The last patients of the week are checking out, and your front desk coordinator gets an email that appears to be from the dentist-owner: "Can you update the payment information for our supply account before you leave? I need it done before the weekend."
The name is right. The tone sounds familiar. And with everyone trying to close out the schedule and get home, the easiest thing to do is simply handle it. There's only one problem: the doctor never sent it.
Your IT security tools can put strong protections in place, but they can't stop every bad click, rushed reply or split-second call. Some decisions still come down to whether the person at the front desk knows what to do when something feels off.
The Assumption That Leaves Practices Exposed
Most practice owners believe cybersecurity lives somewhere behind the scenes. Somebody set up the computers. The antivirus is installed. Dentrix gets backed up. Cybersecurity is "handled."
In reality, your defenses are tested every time a team member decides whether to trust an email, link or request. Those decisions happen every day — at check-in, in billing, in the back office between patients. To truly strengthen your practice's security, your front desk and dental team must know what to do when something doesn't look right.
Technology Can't Make Every Call
Good security tools block a lot of attack attempts before your team ever sees them. But no technology can eliminate every questionable request or make every decision on an employee's behalf.
Today's phishing attacks aren't obvious. They're built to mimic familiar writing styles, reference the labs and suppliers you actually use, and mirror the rhythm of normal practice communication. When an unusual payment request appears to come from the doctor, a dental lab legitimately changes banking details mid-case, or someone asks for patient records they've never needed before — a person must decide what happens next. The employee at the keyboard has to determine in an instant whether they're looking at a scam or an authentic request.
"Be Careful" Isn't a Cybersecurity Plan
Most practices tell staff to watch out for suspicious emails. But what should they do when they find one? Everyone on your team should know:
- Who to contact
- How to verify a request is legitimate — for example, walking down the hall or calling the doctor directly
- Not to click links or download attachments from suspicious messages
- What to do if they already clicked a link or downloaded an attachment
- How to report the issue
Telling everyone to simply "be careful" without a clear next step puts the full weight of a high-stakes decision on the person least equipped to handle it in the moment — often while a patient is standing at the counter.
Assuming your team knows what to do is a liability. A front desk coordinator who isn't sure whether they're bothering the doctor may stay quiet. Someone who fears getting blamed for clicking the wrong thing may wait before reporting it. Hesitation is costly — the time lost while someone decides whether to speak up can turn a manageable incident into locked patient records, a frozen schedule and a HIPAA reporting obligation.
Leadership Sets the Tone
Responsibility starts at the top, because your team takes its cues from the doctor and the practice manager. If the owner routinely skips verification steps because they're between patients, staff learn that speed matters more than process. If it feels uncomfortable to flag suspicious activity, people stay quiet. If someone clicks something they shouldn't and gets publicly reprimanded, everyone learns to hide their mistakes.
Fortunately, the opposite is also true. When leadership normalizes verification, the team takes it seriously. When a front desk coordinator who questions an unusual request is backed up rather than brushed off, the whole practice operates more carefully. When your team trusts leadership, they speak up before a situation becomes a crisis.
Cybersecurity Works Better When Everyone Knows Their Role
Back to that front desk coordinator at 4:17 on a Friday afternoon.
The goal isn't to make your team paranoid about every email between patient check-ins. It's to make sure that when something feels off, they know exactly what to do, who to ask and how to verify. Speaking up should always feel like the right move.
Your front desk and dental team don't need to become cybersecurity experts to help protect your practice. They need clear expectations, good habits and the confidence to flag when something doesn't look right.
Creating that kind of security culture takes more than an annual training session. It requires the right safeguards, practical processes and ongoing guidance to keep your practice prepared as threats change — especially when there's no dedicated IT person on staff to own it.
Frequently Asked Questions
What is security awareness training for a dental team?
It's structured, ongoing education that teaches your front desk and dental team to recognize phishing, social engineering and other threats — and gives them a clear process for verifying and reporting suspicious activity. Done well, it turns your team into an active layer of defense for patient records and imaging.
Do you offer HIPAA-compliant IT services for dental offices in Salt Lake City?
Yes. Qual IT provides HIPAA IT support for dentists in Salt Lake City, including email security, phishing protection, staff training, encrypted backups of practice management and imaging data, and incident response planning aligned with HIPAA requirements.
How does an IT partner help a practice build a security culture?
A partner like Qual IT identifies your gaps, implements the right safeguards around systems like Dentrix, Eaglesoft and your imaging software, sets up practical verification and reporting processes, and provides the ongoing training and guidance that keeps security habits current as threats evolve.
You Don't Have to Manage It Alone
That's where the right IT partner comes in. Qual IT helps practices take the guesswork out of cybersecurity by identifying gaps, strengthening protections and helping every team member understand the role they play in keeping patient data secure.
We work with Salt Lake City dental practices to keep systems running and patient data secure. Cybersecurity is everyone's responsibility — but you don't have to manage it alone.
Schedule a 10-minute discovery call with Qual IT to find the gaps in your current approach and how to address them. Book your discovery call here.